If you run a business in Belton, Temple, or anywhere along the I-35 corridor, there is a good chance your cyber insurance renewal in 2026 asked harder questions than it did two years ago. Managed IT services Belton owners rely on do more than fix computers; they help you prove to an underwriter that your business is a safe risk, so you can qualify for coverage and still have it when you file a claim.
Quick Answer: To qualify for cyber insurance, insurers expect you to show working controls, not good intentions: multifactor authentication, tested backups, endpoint protection, patching, and written policies. A managed IT partner builds, documents, and maintains those controls so your application answers are true on the day you sign and on the day you claim.
Key Takeaways
- Cyber insurance applications now work like an audit. Underwriters ask what you actually do, and they can verify it.
- A wrong answer on your application can put a claim at risk, even if the mistake was an honest one.
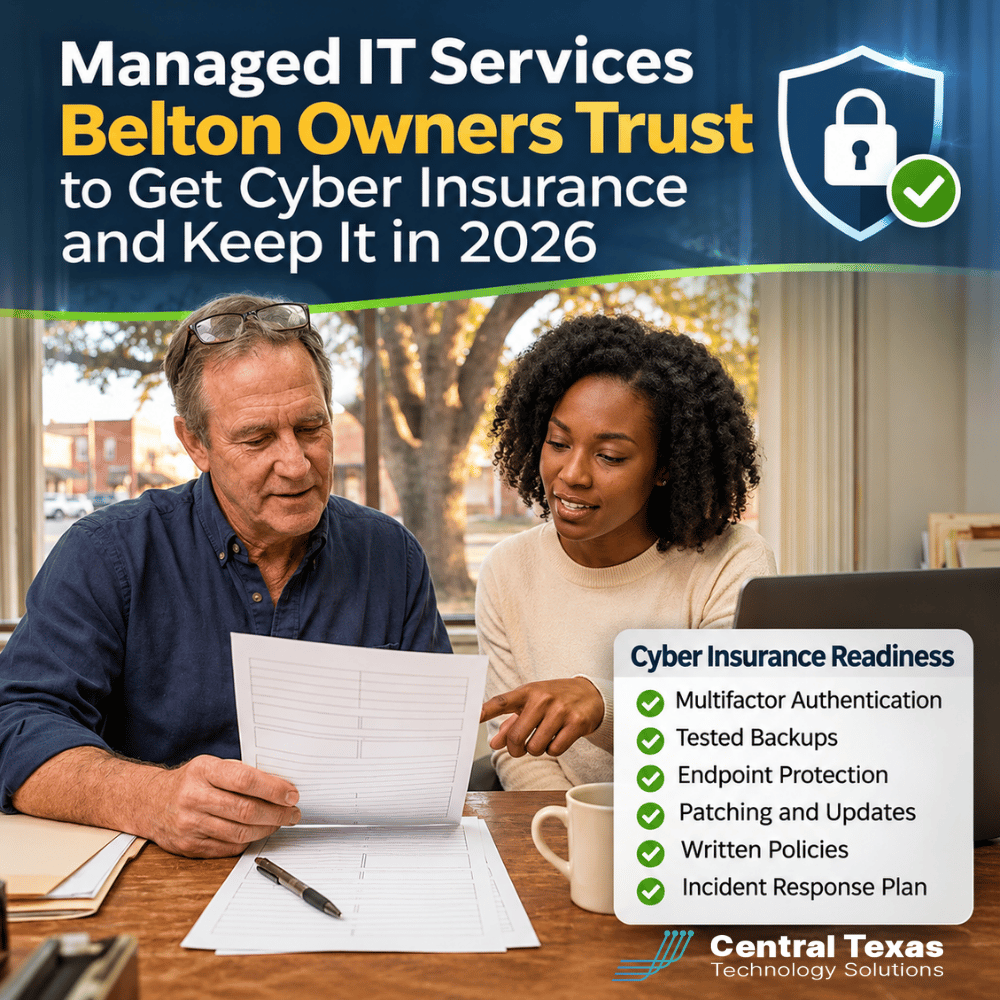
- The same short list of controls shows up on almost every application: MFA, backups, endpoint protection, patching, training, and an incident plan.
- Documentation matters as much as technology. If you cannot show it, it may as well not exist.
- Qualification is a yearly habit, not a one time project, and a managed partner keeps the evidence current.
What's at Stake When it Comes to Cyber Insurance
Most owners think of cyber insurance as a safety net. It is, but it is a net with conditions. The policy is a contract, and the application is the part of that contract where you describe how your business protects itself. If you say every account uses multi factor authentication and a forgotten service account does not, you have created a gap between what you promised and what is true.
That gap is where claims get complicated. After an incident, the insurer looks at how it happened. If the facts do not match the application, the carrier may reduce the payout, dispute it, or in the worst case deny it. For a business with 10 to 250 employees, a single ransomware event can cost more than a year of profit. Losing the coverage you counted on at that moment is the real risk.
There is a second cost that rarely gets discussed: the cost of not qualifying at all. Some owners find at renewal that their premium jumps, their coverage limits shrink, or the carrier declines to renew. Then they are scrambling to install controls in a few weeks, under pressure, while still trying to run the business.
Why Central Texas Businesses Face This Challenge
Central Texas is full of exactly the kind of business insurers watch closely: medical and dental practices in Temple and Belton, law and accounting firms in Georgetown and Round Rock, contractors and engineering firms who handle bid documents and client drawings, and nonprofits that hold donor records. These organizations hold sensitive data, but many have a small internal team or a single person who wears the IT hat on top of another job.
That is a hard position. The person who answers the cyber insurance questionnaire is often the office manager or the owner, and the questions sound technical. Is your endpoint detection centrally managed? Do you enforce MFA on privileged accounts? How often do you test restores? It is easy to answer from memory and get something wrong.
Growth adds pressure too. Belton and the surrounding Bell County communities keep adding businesses and new hires. Every new employee, laptop, and cloud app is something that has to be covered by the controls you described on your application.
How CTTS Helps You Qualify for Cyber Insurance
We have served Central Texas since 2002, and we answer the phone in 3 rings. The way we help with cyber insurance is simple: we make the controls real, we document them, and we keep them current. We do not write the policy and we do not replace your insurance agent. We make sure the technology facts your agent and carrier ask about are true.
For clients on Complete Care Coverage, this work is part of the monthly agreement. Monitoring, patching, endpoint protection, backup verification, and account security are already running, so the application is mostly a matter of pulling the evidence. For businesses with an internal IT person, Co-Managed IT extends our remote management and monitoring, documentation platform, and ticketing tools to that team so the evidence gets built without adding headcount.
In practice, a cyber insurance readiness review with us looks like this:
- We walk through your current or draft application line by line and mark every answer as confirmed, partly true, or not true.
- We close the gaps that matter most, usually MFA coverage, backup testing, and endpoint protection on every device.
- We build a simple evidence folder: screenshots, reports, and policies you can hand to your agent.
- We schedule the yearly refresh so renewal is a calm conversation instead of a fire drill.
The Cyber Insurance Readiness Checklist Owners Should Know
Do I need multifactor authentication on every account?
Yes, or as close to every account as you can get. MFA is the control insurers ask about first because stolen passwords are behind so many incidents. Pay special attention to email, remote access, administrator accounts, and the accounts your vendors use to reach your systems. A policy that says "most users" is weaker than one that says "all users with no exceptions."
Are backups really enough to satisfy an insurer?
Not unless they are tested and protected. Backups that sit on the same network as your servers can be encrypted by the same ransomware that hits everything else. Insurers want to see copies that are separated from your main environment and a record that you have restored from them recently. A backup you have never restored is a hope, not a control.
What does endpoint protection mean to an underwriter?
It means modern, centrally managed protection on every laptop, desktop, and server, with someone watching the alerts. Old style antivirus that updates once a day and nobody reviews rarely satisfies current questionnaires. The word to listen for is managed. A tool on a device is helpful. A tool that a trained team monitors is what carriers count.
How quickly do I have to patch systems?
There is no single number, but the expectation is that critical updates go in promptly and you can show it. A managed patching process produces reports that prove what was updated and when. Without it, you are relying on staff to remember, which is how a forgotten server becomes the way in.
Do I need a written incident response plan?
Yes. Many applications ask whether you have one, and a claim goes more smoothly when you do. The plan can be short: who to call first, who makes decisions, how to reach your insurer's claims line, and where the backups are. Write it down and keep a printed copy, because email may be the first thing you lose.
Common Mistakes That Put Coverage at Risk
The most common mistake is optimism. Someone answers yes to a question because the control exists somewhere, even though it does not cover everyone. The second is treating the application as a form to finish quickly instead of a statement of fact. The third is forgetting that the application describes a moment in time. If you added an office, switched a vendor, or onboarded twenty people since you signed, the picture may have changed.
A fourth mistake is assuming the insurance agent will catch technical problems. Agents are skilled at coverage, but they are not looking inside your network. That is the gap a managed IT partner fills, working beside your agent instead of replacing them.
Finally, many owners wait until renewal to think about any of this. By then, there is little time to fix a missing control. The better rhythm is a short review a few months before renewal, so there is room to close gaps and your premium conversation starts from strength.
Take the Next Step
If your renewal is coming up, or you are applying for coverage for the first time, start with the facts. Our Executive IT Risk Assessment shows you exactly where your business stands against the controls carriers ask about, in plain language, with a clear list of what to fix first. There is no pressure and no jargon. You will leave knowing which answers on your application are solid and which need work.
Schedule a free strategy session with CTTS and bring your most recent application or renewal notice. We will go through it together, owner to owner, and give you a straight answer.
Have Questions? We've Got Answers
Does having a managed IT provider lower my cyber insurance premium?
It can help, but results vary by carrier and by your overall risk. What a managed provider reliably does is help you meet the underwriting requirements and prove them, which keeps you eligible and strengthens your position when you negotiate a renewal.
What happens if I answered the application incorrectly?
Talk to your insurance agent as soon as you notice. Carriers can treat inaccurate answers seriously, so it is better to correct the record and fix the gap than to hope it never comes up. We can help you confirm what is actually in place so the correction is accurate.
Can a small business in Belton or Temple realistically meet these requirements?
Yes. The controls insurers ask about are well understood and affordable when they are managed for you. Our approach is built for organizations with 10 to 250 employees, so you get the same discipline larger companies have without hiring a full security team.
Contact CTTS today for IT support and managed services in Austin, TX. Let us handle your IT so you can focus on growing your business. Visit CTTSonline.com or call us at (512) 388-5559 to get started!